Platform
From uncertainty to an action plan, in one place
The NIS2PME platform turns the regulatory framework into a concrete journey: diagnosis, controls, evidence and reports, all in language management understands. Open-source, bilingual and designed for SMEs.
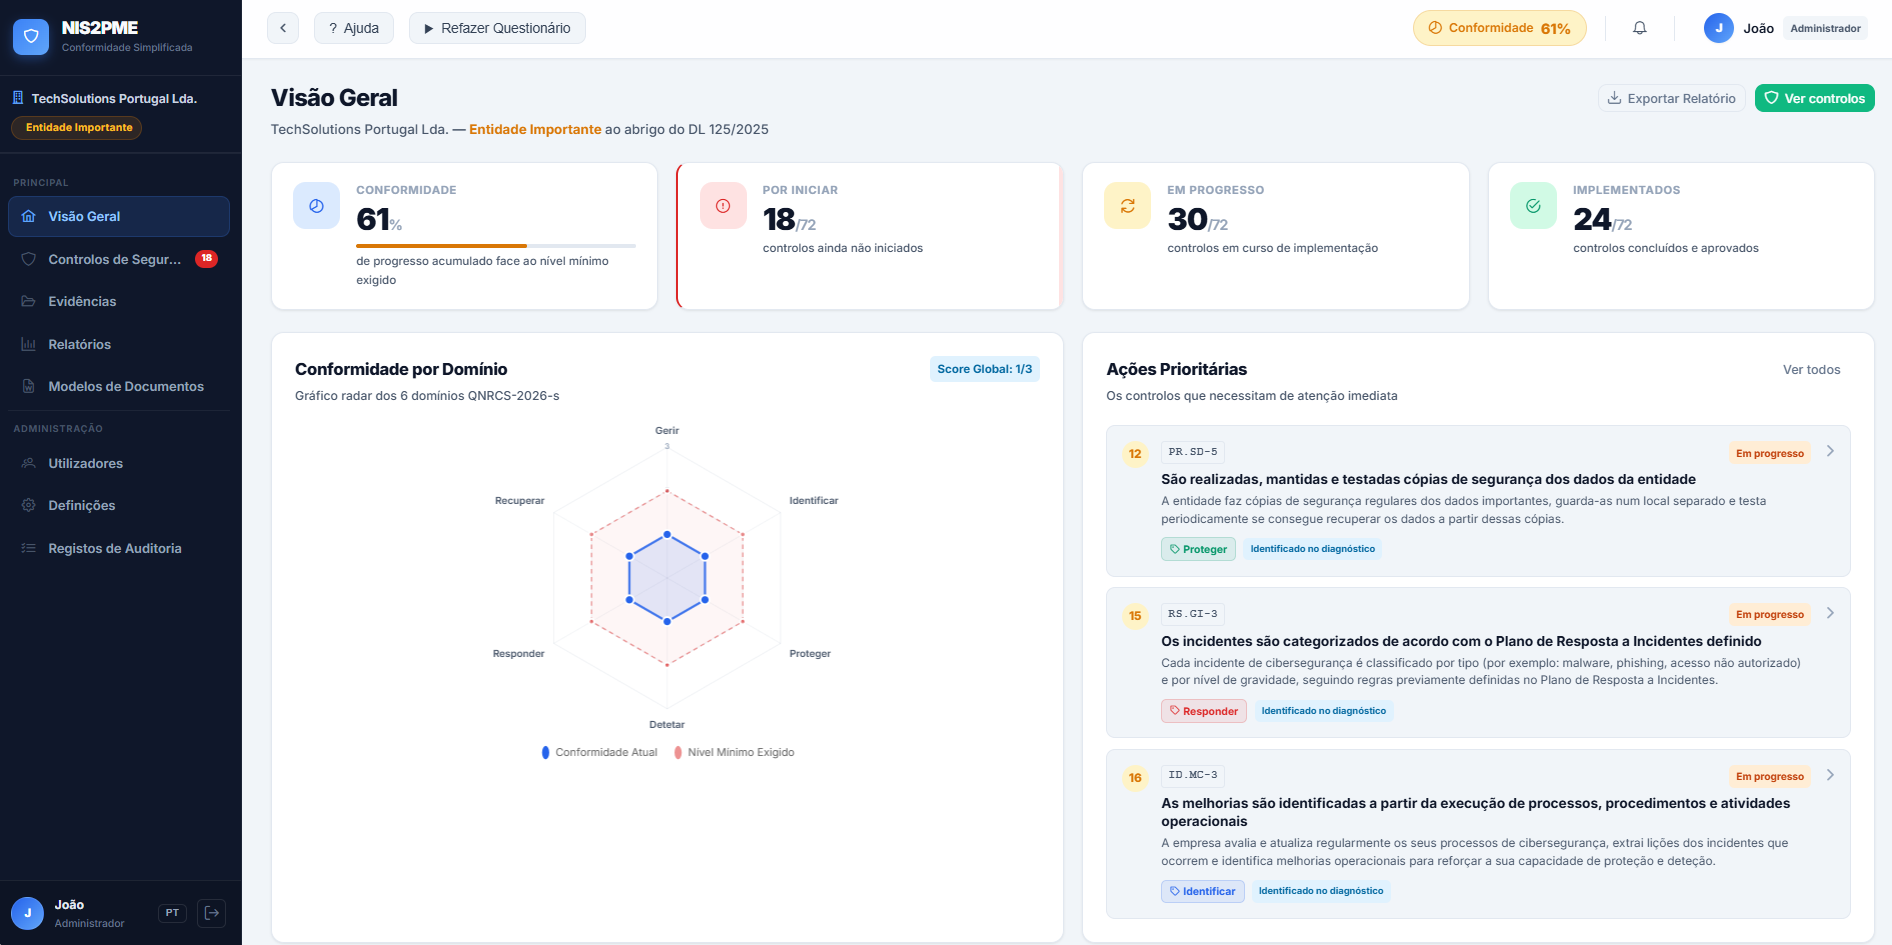
Features
Everything an SME needs for NIS2 compliance
Guided diagnosis
A 10-question questionnaire in plain language, mapped to the most common vulnerabilities in SMEs. At the end, you get a priority action plan: the controls to address first.
Controls tailored to your level
Filter the 107 controls by your entity's level and delegate the applicable measures in one step: whoever implements them sees only those. Each control has an implementation guide, with steps, evidence examples and estimated effort.
Evidence management
Attach documents and proof to your controls: one piece of evidence can serve several. When supervision arrives, everything is organised and ready to present.
Incidents and deadlines
Assess whether an incident is significant with four simple questions, track the deadlines for notifying the authority and get warnings before they expire. The PDF report comes pre-filled.
Templates and reports
14 policy and plan templates, in Word, and a compliance report in PDF to present to management, auditors or authorities.
Team and trail
Five roles with adjustable permissions, mandatory two-factor authentication and an audit log where any change is detected.
Premium plan
Automate what is manual. Verify what is declared.
The core tells you what to do and keeps the proof. Premium takes on the heaviest work: inventory, risk and suppliers with a ready-made method, import of what you already have in other tools, technical checks and AI analysis.
Asset inventory
With dependencies and criticality classified through simple questions.
Risk analysis
Over 30 ready-to-use scenarios, linked to QNRCS controls.
Suppliers
Due diligence and supply-chain risk assessment.
Import and cross-checking
What you already have in other tools, brought together and cross-checked in one place.
Technical checks
Confirms what is declared and warns you when reality contradicts it.
AI analysis
Reviews documentation and evidence and suggests how to strengthen them.
Proportional by law
The right level for your entity, no more, no less
The compliance level (Basic, Substantial or High) results from the regulatory classification defined by the CNCS, not from the platform. The entity indicates its level, and NIS2PME measures compliance against the minimum measures for that level.
Basic
The QNRCS entry level: the fundamental cybersecurity hygiene practices.
Substantial
Reinforced requirements for entities with greater risk exposure and impact.
High
The most demanding level, for the largest and most critical entities.
The QNRCS defines 107 controls in total. Each compliance level requires a minimum subset (43, 75 or 92 measures); the remaining ones are available to those who want to go beyond the required minimum. The platform covers all 107.
The 6 QNRCS objectives
Always up to date: NIS2PME is aligned with Regulation 756/2026 (in force), which establishes the QNRCS and the minimum cybersecurity measures per compliance level, and follows CNCS updates and guidance. You can start today: this is what the law requires.
How it works
Four steps to demonstrable compliance
Answer the diagnostic questionnaire
10 simple questions, mapped to the most common vulnerabilities in SMEs. No technical knowledge required.
Get your priority action plan
Each answer is linked to QNRCS controls. At the end, you know exactly which ones to analyse and implement first.
Implement the controls with guidance
Each control explains the what, the why and the how, with document templates and built-in evidence management.
Track, demonstrate and improve
Progress dashboards and exportable reports that demonstrate your compliance to management and authorities.
Verifiable trust
In a cybersecurity platform, being able to read the code is the argument
The NIS2PME core is open-source under the AGPL-3.0 licence. No black boxes, no vendor lock-in: deploy on your infrastructure and keep full control of your data.
Auditable code
The entire core is published on GitHub. Anyone, including your IT technician, can verify exactly what the platform does with your data.
On-premises with Docker
Deploy on your own infrastructure with Docker, using a start-up script and a step-by-step guide. Your company's data never leaves your control.
Actively developed
Continuous improvements and ongoing alignment with CNCS guidance. Follow along and contribute on GitHub.
See where your company stands, no strings attached
Run the 14-day evaluation trial or deploy the on-premises version. Either way, the diagnosis takes minutes.